
Introduction
A securities company licensed by the Financial Supervisory Authority to conduct securities trading and classified as Class 2 under the IFR needed to ensure an independent and effective risk management function. To ensure the right expertise and a proportionate solution, the company chose to outsource the function to an external party, which was NFC hired for the assignment.
In his role as the company’s risk management function, he is responsible NFC for establishing, in close collaboration with the board and management, a structured and long-term sustainable risk management framework within the company. At the initial stage of his assignment, the company faced the implementation of the new regulatory framework. DORA, This meant that operational resilience and ICT risks were prioritized as part of a broader effort to strengthen the company’s risk management.
Background
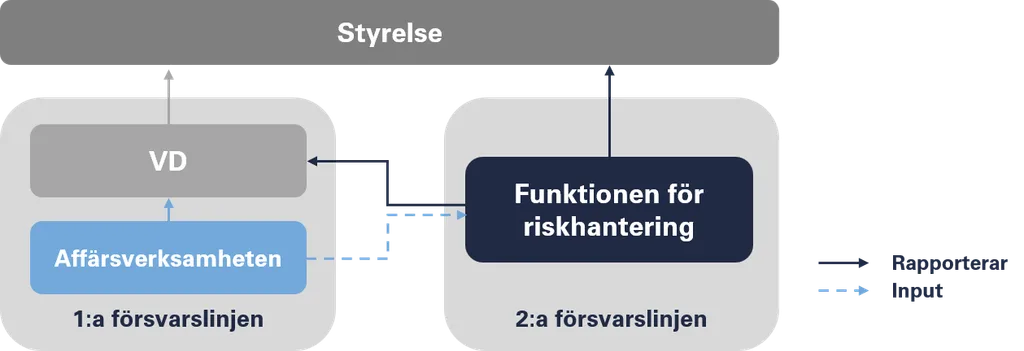
Current regulations require that securities companies have an independent risk management function. Since the business did not justify a full-time resource for the function, outsourcing to an external party was a cost-effective solution, while ensuring the right expertise was available. Furthermore, it was important for the company that the function could work closely with the business and have good insight into the daily operations to identify new and changing risks early on.
Against this background, we were hired NFC to provide the company with the functions of risk management. The chosen approach gave the company access to relevant expertise to support its risk management and governance efforts, while the internal risk management could be strengthened through ongoing support, advice, and training in risk-related areas. The choice was made NFC thanks to our experienced employees and methodological approaches, where a close dialogue with the business is combined with ongoing reporting to management and the board.
Execution
The initial phase of the II project involved a review of the company’s existing risk management framework against applicable regulations, along with a self-assessment of risks, to establish a clear picture of the risk profile of the business. In light of the upcoming DORA regulations, a gap analysis was also conducted to identify development needs related to operational resilience and ICT risks. These analyses formed the basis of the first annual plan, in which the most prioritized areas were addressed.
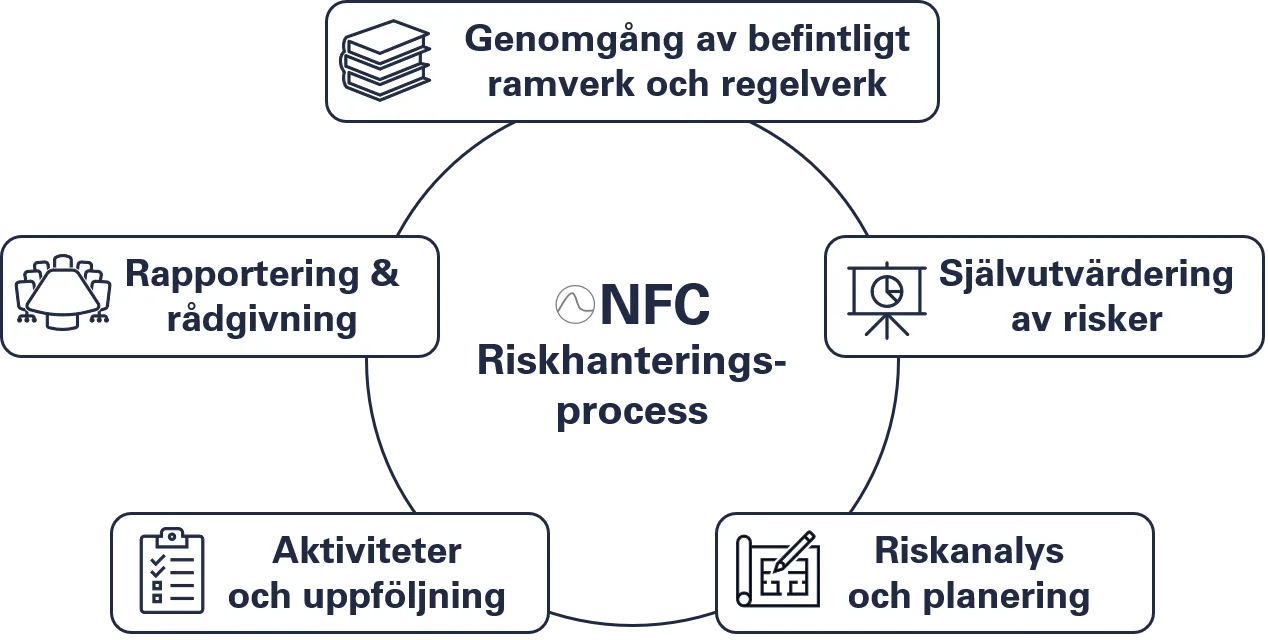
As an external risk management function, we work NFC according to a structured and recurring process to ensure effective and business-oriented risk management over time. Our work is based on a continuous cycle where risks are identified and analyzed, prioritized in an annual plan, managed through targeted control activities, and monitored through reporting and dialogue with management and the board.
A central part of the working method is the annual self-assessment of risks, which is carried out together with key personnel within the company. This forms the basis for risk analysis and the prioritisation of activities for the coming year, ensuring that focus is directed towards the most significant risk areas. Based on this, an annual plan (the ”risk plan”) is prepared, which includes both recurring elements, such as the development of internal capital and risk assessment (IKRU), and more targeted control and follow-up measures.
The implementation of the risk plan includes ongoing control activities, follow-up of identified deficiencies, and continuous reporting to the board and management. As an integrated part of the approach, it NFC also participates in board meetings to contribute an independent risk perspective and provide ongoing advice and support in current decisions and questions.
Outcome
The initial analyses and checks identified a number of shortcomings and areas for development. These were translated into concrete action proposals that were prioritized in the first annual plan based on the level of risk, to be subsequently followed up in the ongoing risk management work. The ongoing reporting to the board also provided the management with a clearer picture of the company’s risks, strengthening the decision-making basis in business-related matters.
Among the identified improvement areas were specific needs related to adapting to DORA, where the company lacked a structured mapping of information and ICT assets, as well as sufficient expertise regarding ICT risks at the board level. To address this, among other things, a targeted board training was conducted, as well as a workshop in which assets were identified and documented in a register that can be updated continuously.
As part of the assignment, a review of the company’s regulatory reporting was also conducted. During the initial review, certain minor deficiencies were identified, which were corrected before the subsequent reporting occasion. This contributed to strengthening the quality and reliability of the reporting as well as reducing the risk of regulatory action. Overall, the assignment helped establish a more structured, proactive, and risk-based management of the business. By integrating the risk perspective into key processes and translating identified risks into concrete measures, not only regulatory compliance was strengthened, but also the company’s internal control and ability to make well-founded business decisions.
Do you need an experienced and independent risk management function? Read more about our risk management and control services or contact us directly and we’ll tell you more!


